Featured tool
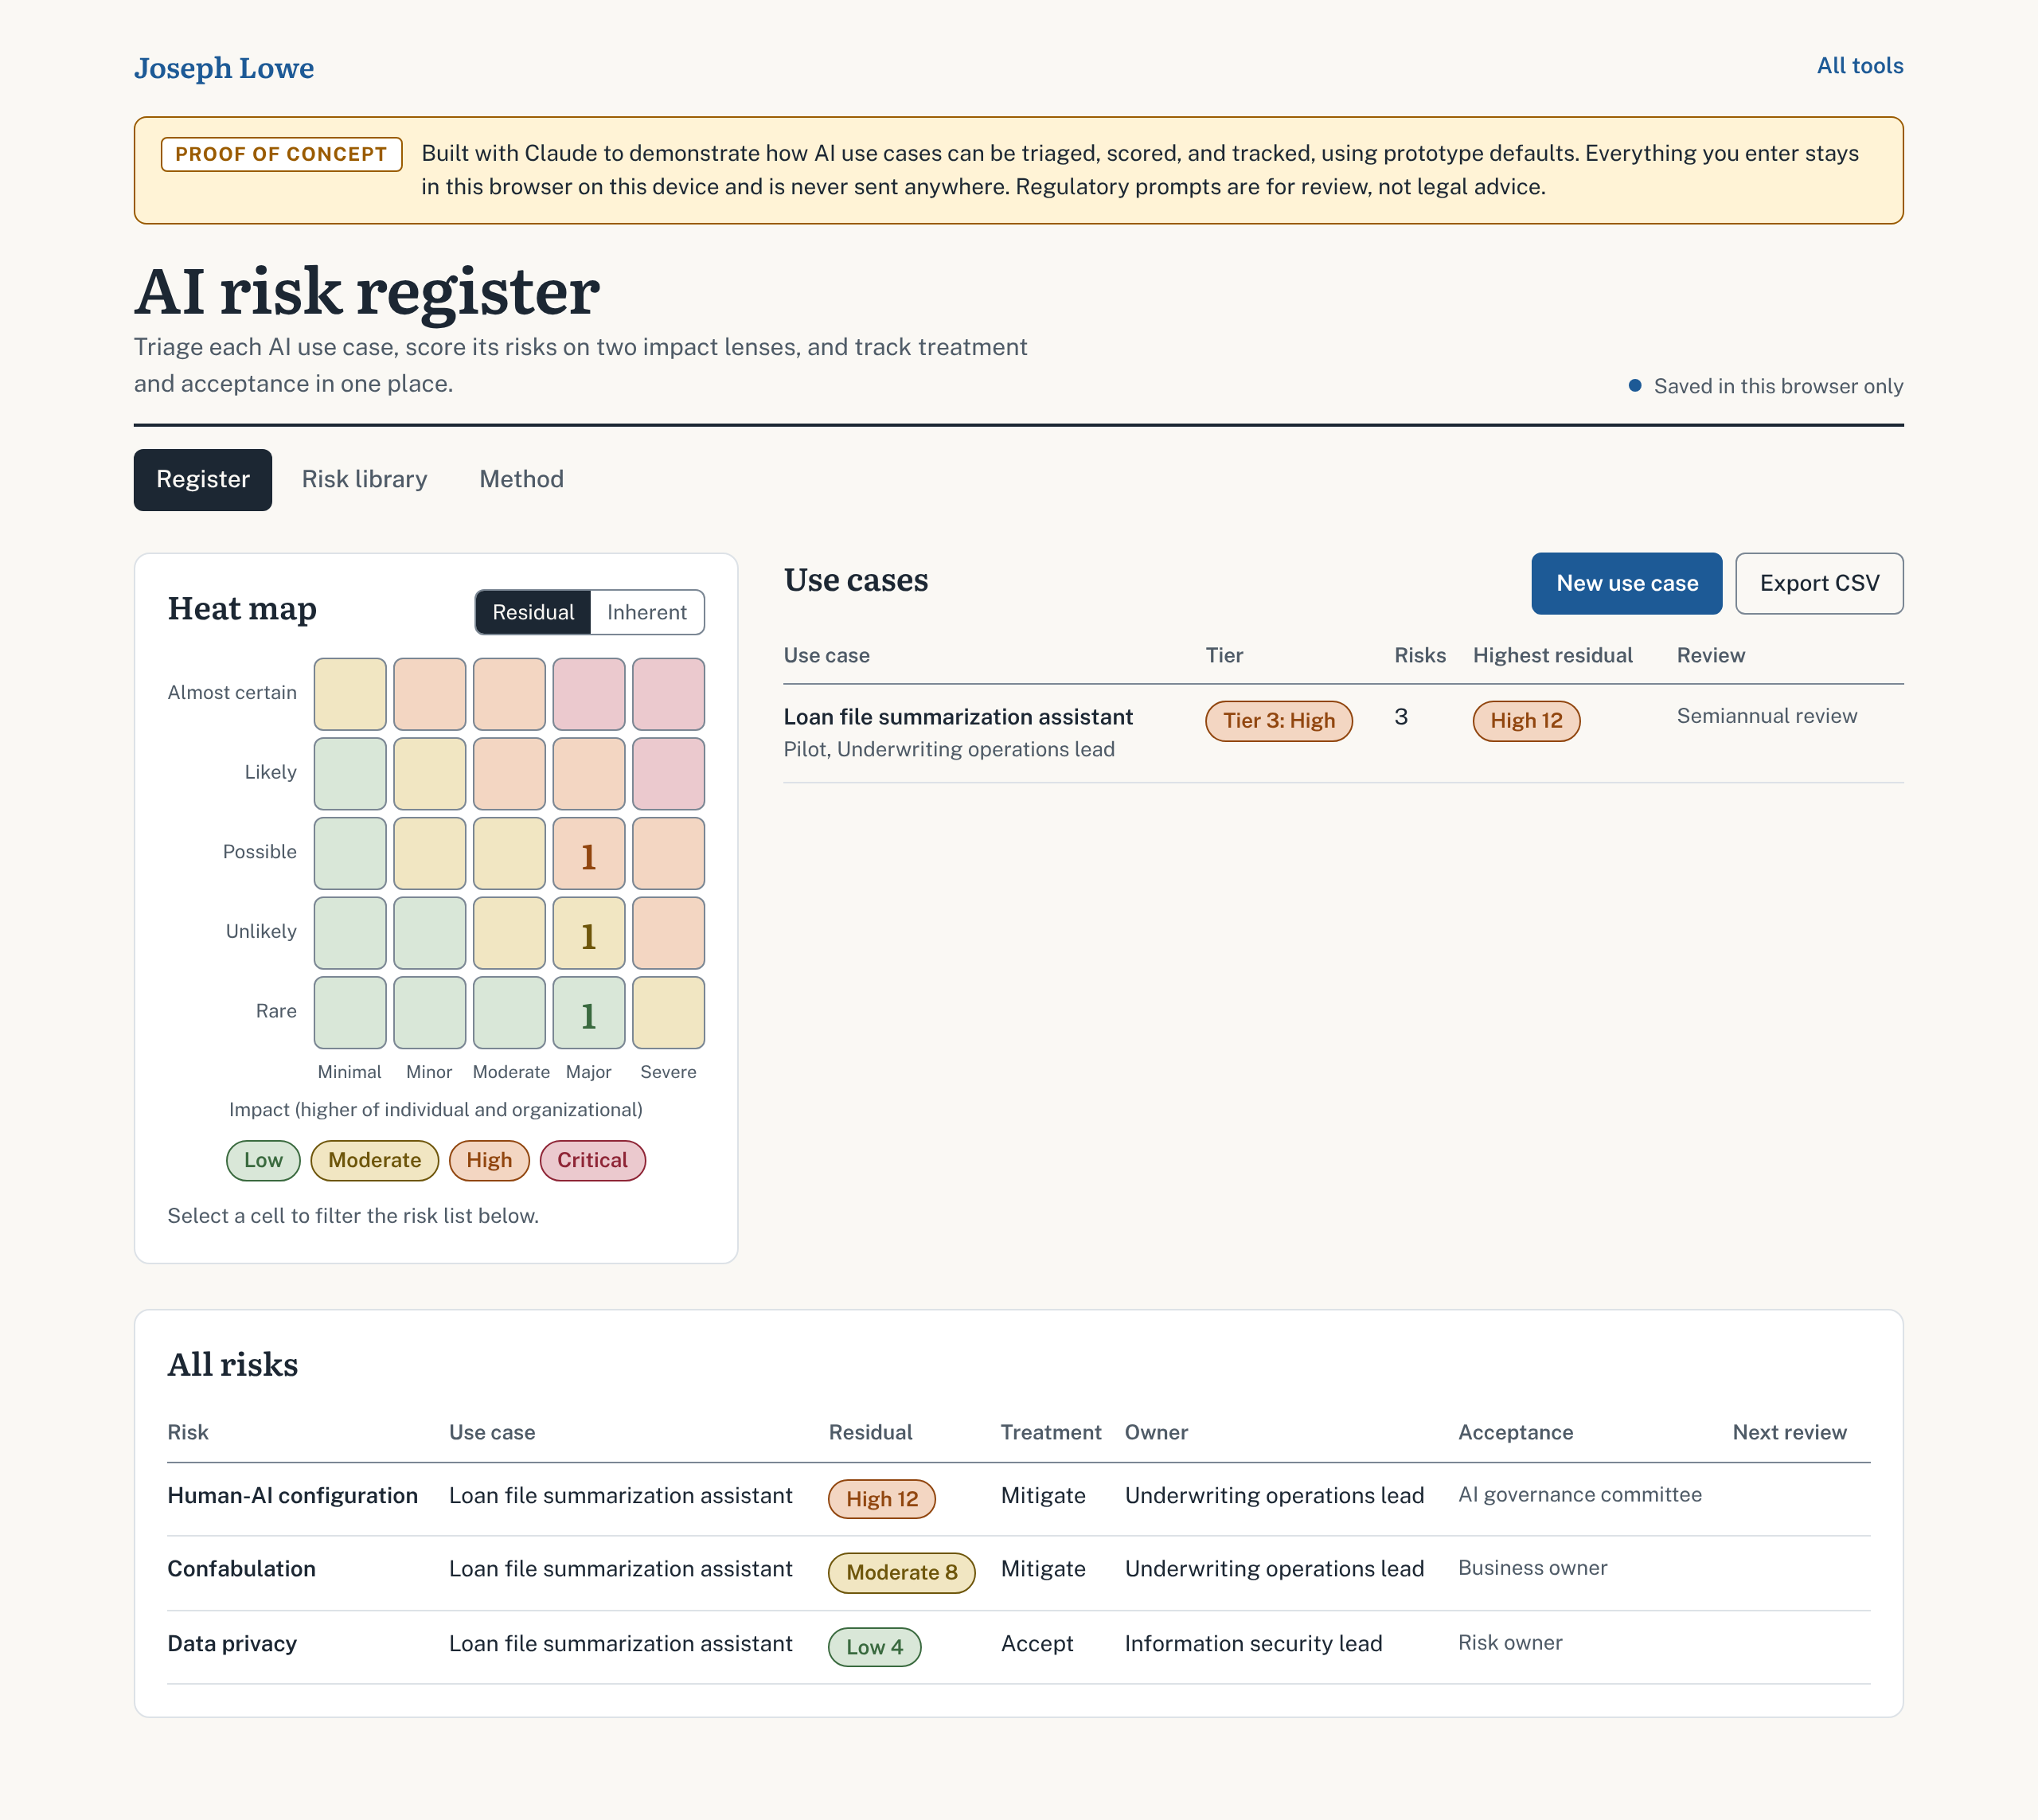
AI Risk Register and Assessment
Triage each AI use case, score its risks on two impact lenses, and track treatment and acceptance in one place.
Selected results
-
Nine consecutive unqualified SOC opinions.
I settled the control objectives with our external auditor each cycle, drafted the System Description with system and program owners, and reviewed evidence before it reached the auditors, achieving unqualified SOC 1 and SOC 2 opinions every year from 2017 through 2025.
-
25% less evidence-collection effort.
I directed my team's adoption of AI-assisted and automated evidence-collection utilities, cutting the hours our evidence providers logged by 25% in the 2025 audit cycle compared with the prior two-year average.
-
A security policy and standards library.
I directed the AI-assisted development of a security policy and standards library: I scoped the documents needed, crafted the prompts that drafted them, and reviewed the content for accuracy before a wider team iterated on, edited, and approved it.
-
Client assurance for 50+ clients a year.
I owned client due diligence for more than 50 clients a year, completing due diligence and security control validation requests and deciding what evidence could be shared while protecting confidential company and customer information.
-
Every critical and high finding remediated within SLA.
I triaged findings hands-on with engineering and IT teams, applied CVSS directly, and directed remediation so every critical and high finding met the corporate-published SLA, with none going past due.
-
AI risk assessment in practice.
I started running AI risk assessments in September 2025, extending our established practice for vulnerability management and software security analysis, and helped initiate the onboarding and review process for our AI system inventory.
-
Built a RAG tool for due diligence.
I built and operated a retrieval-augmented generation (RAG) tool for client due diligence questionnaires, with human-in-the-loop review, cutting turnaround from multiple weeks to days.
If you are building or strengthening a security, risk, or compliance program, I would welcome the conversation.
Contact